Sovereign security engineering

Nova.

AI red and purple team agents. On-premises, air-gapped, and auditable.

Book a call

Dr Andrea Tassi · Founder  ·  An independent, founder-led venture.

operator@nova-appliance: nova
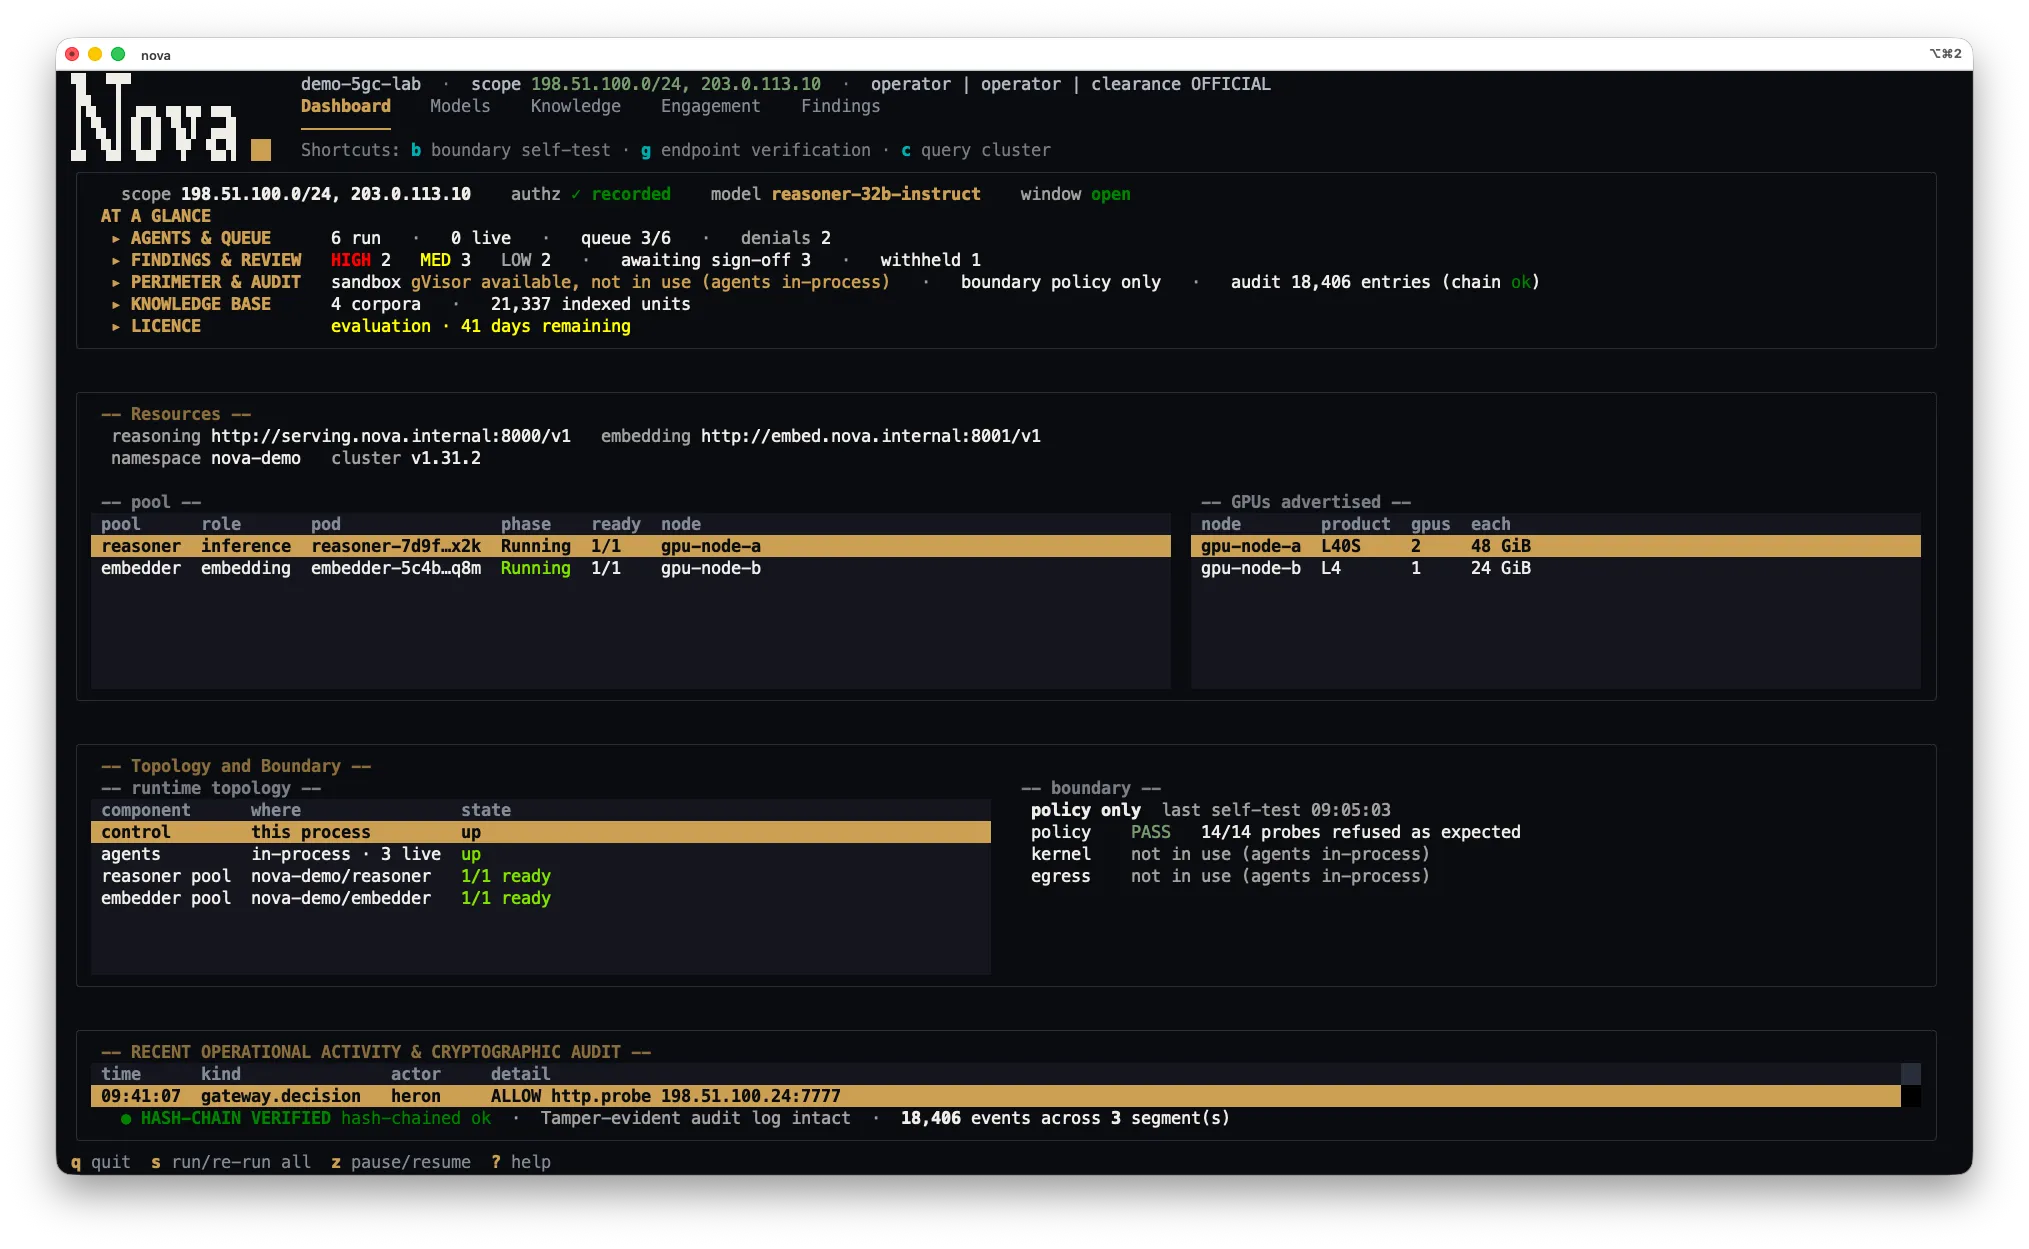
Nova terminal interface, Dashboard view: Scope, agents, findings and audit at a glance
Dashboardassets/screens/1.webp
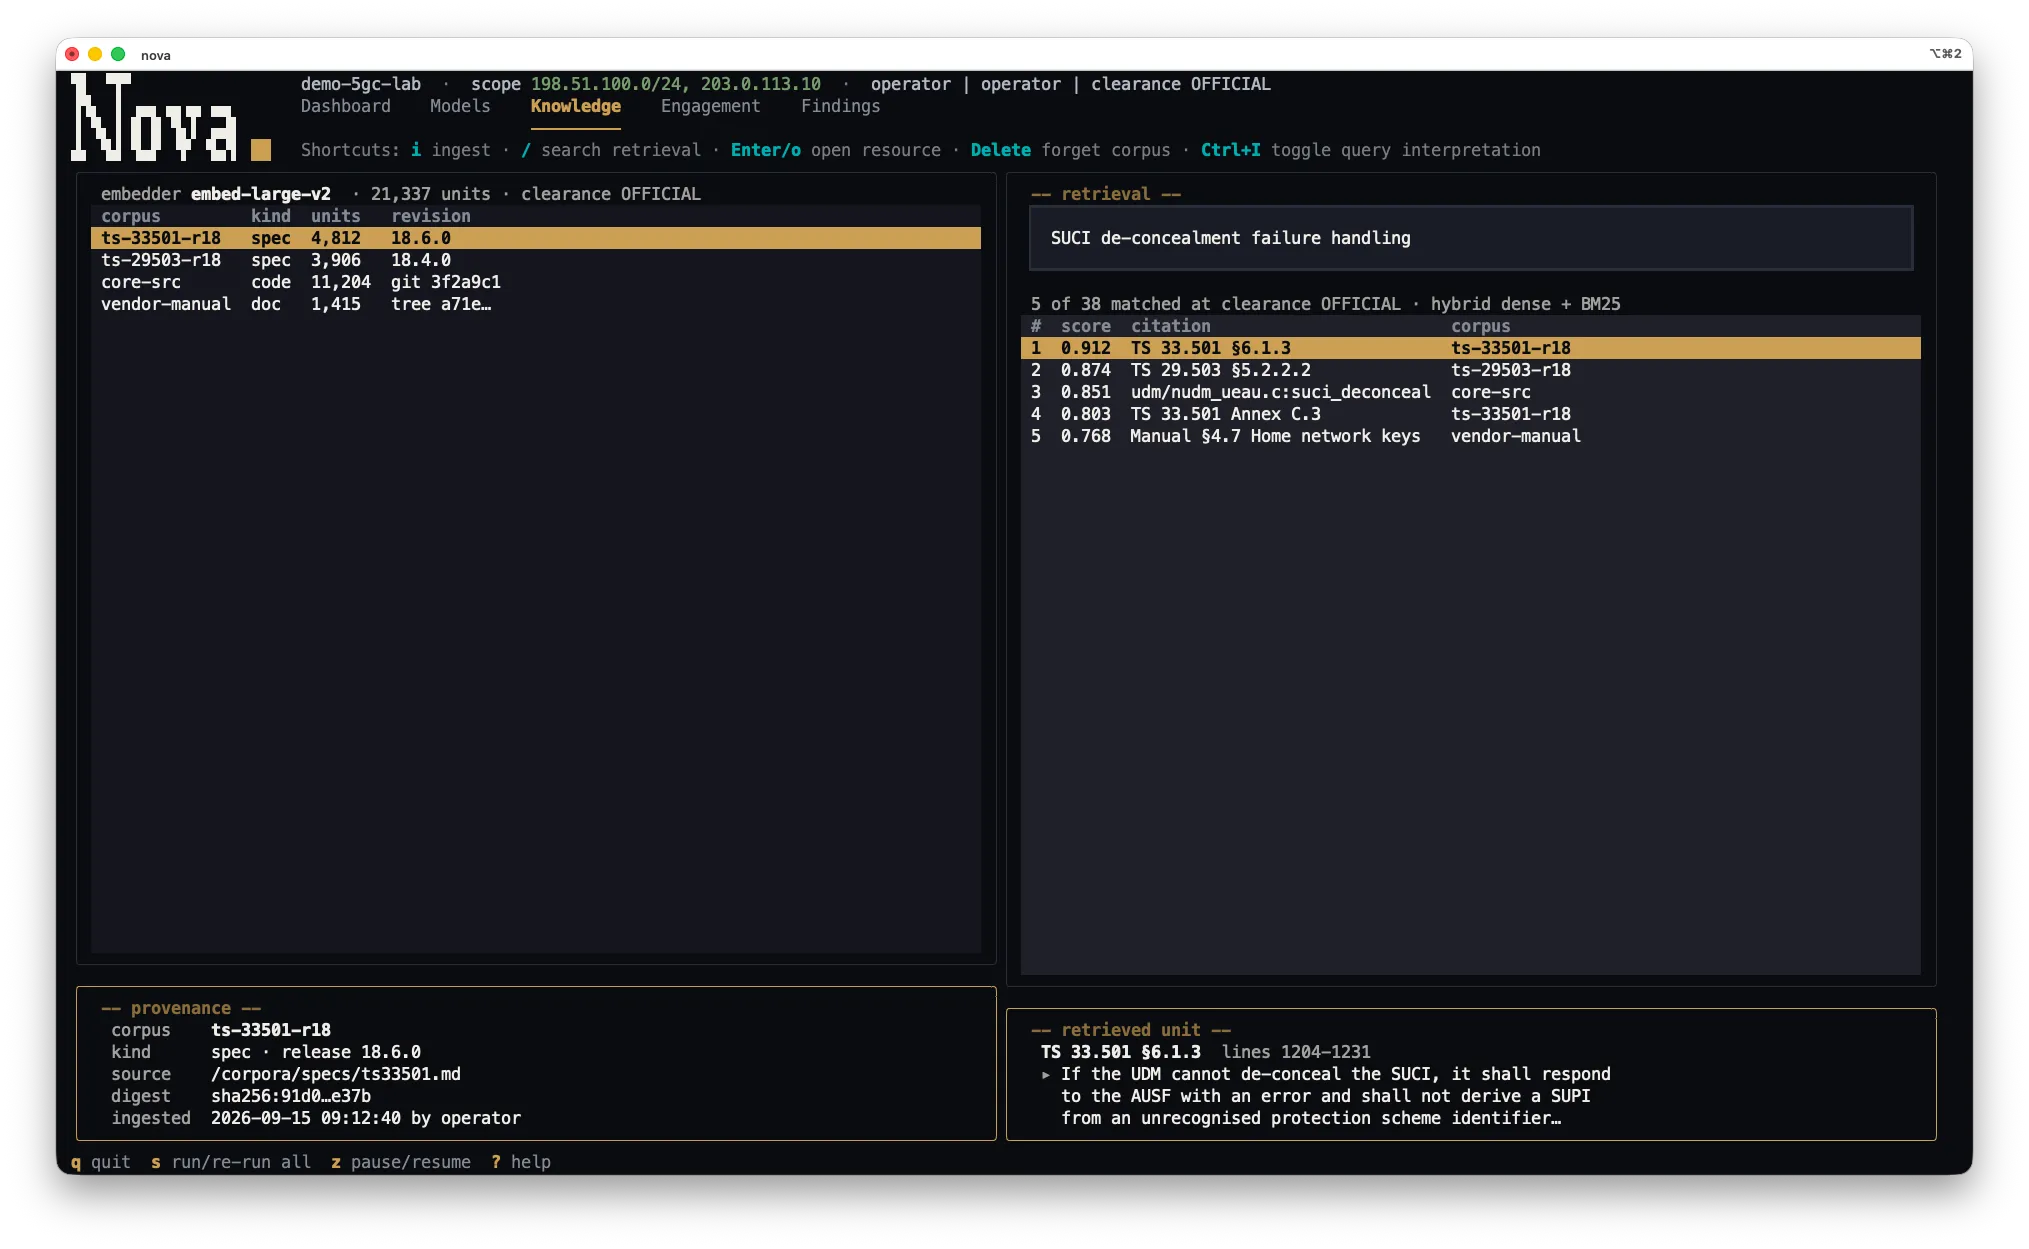
Nova terminal interface, Knowledge view: Hybrid retrieval over specifications, manuals and code, with provenance
Knowledgeassets/screens/3.webp
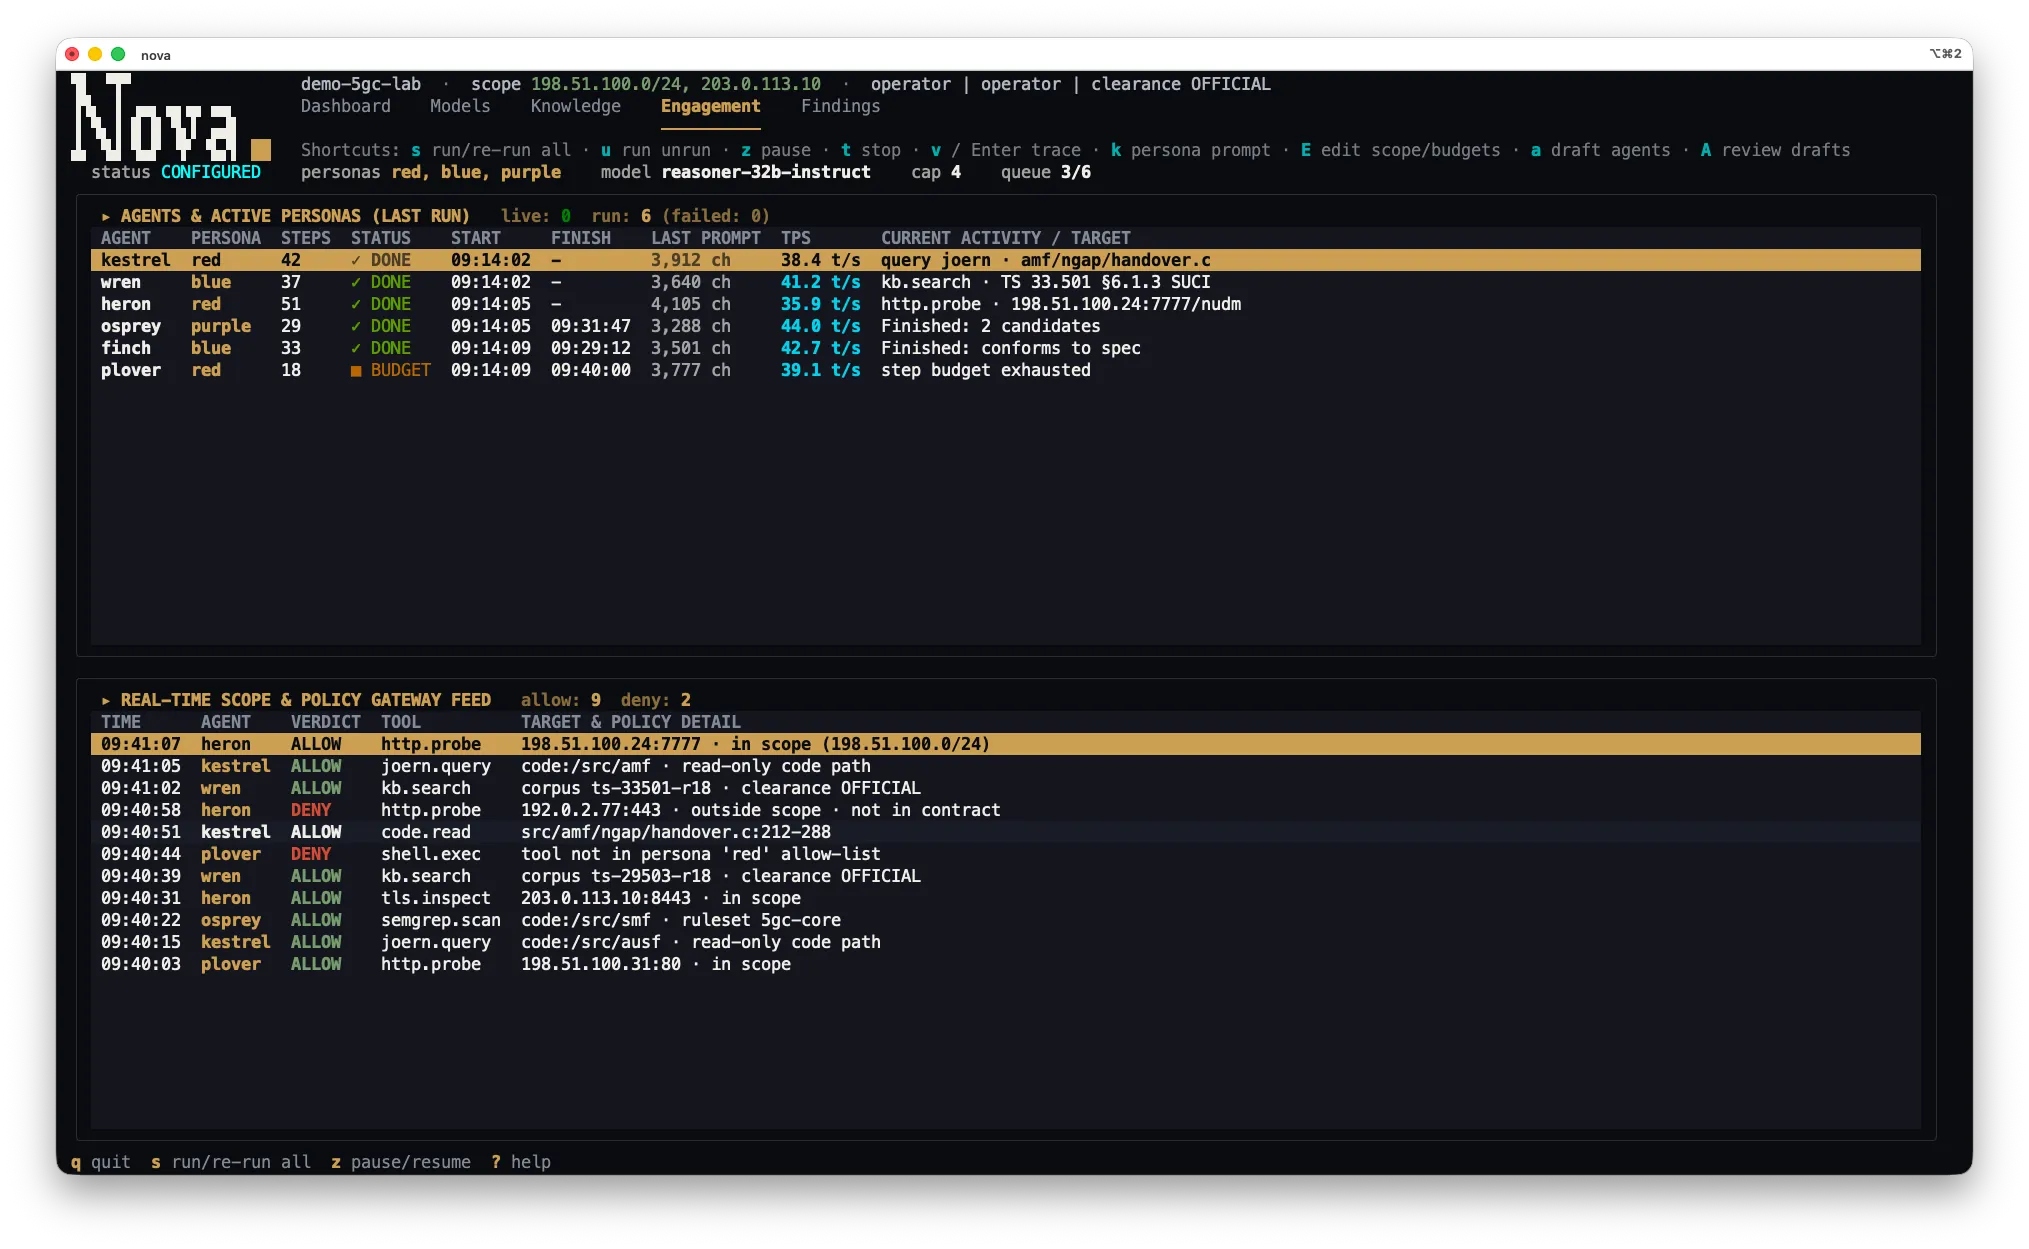
Nova terminal interface, Engagement view: Agents at work, with every policy decision in a live feed
Engagementassets/screens/4.webp
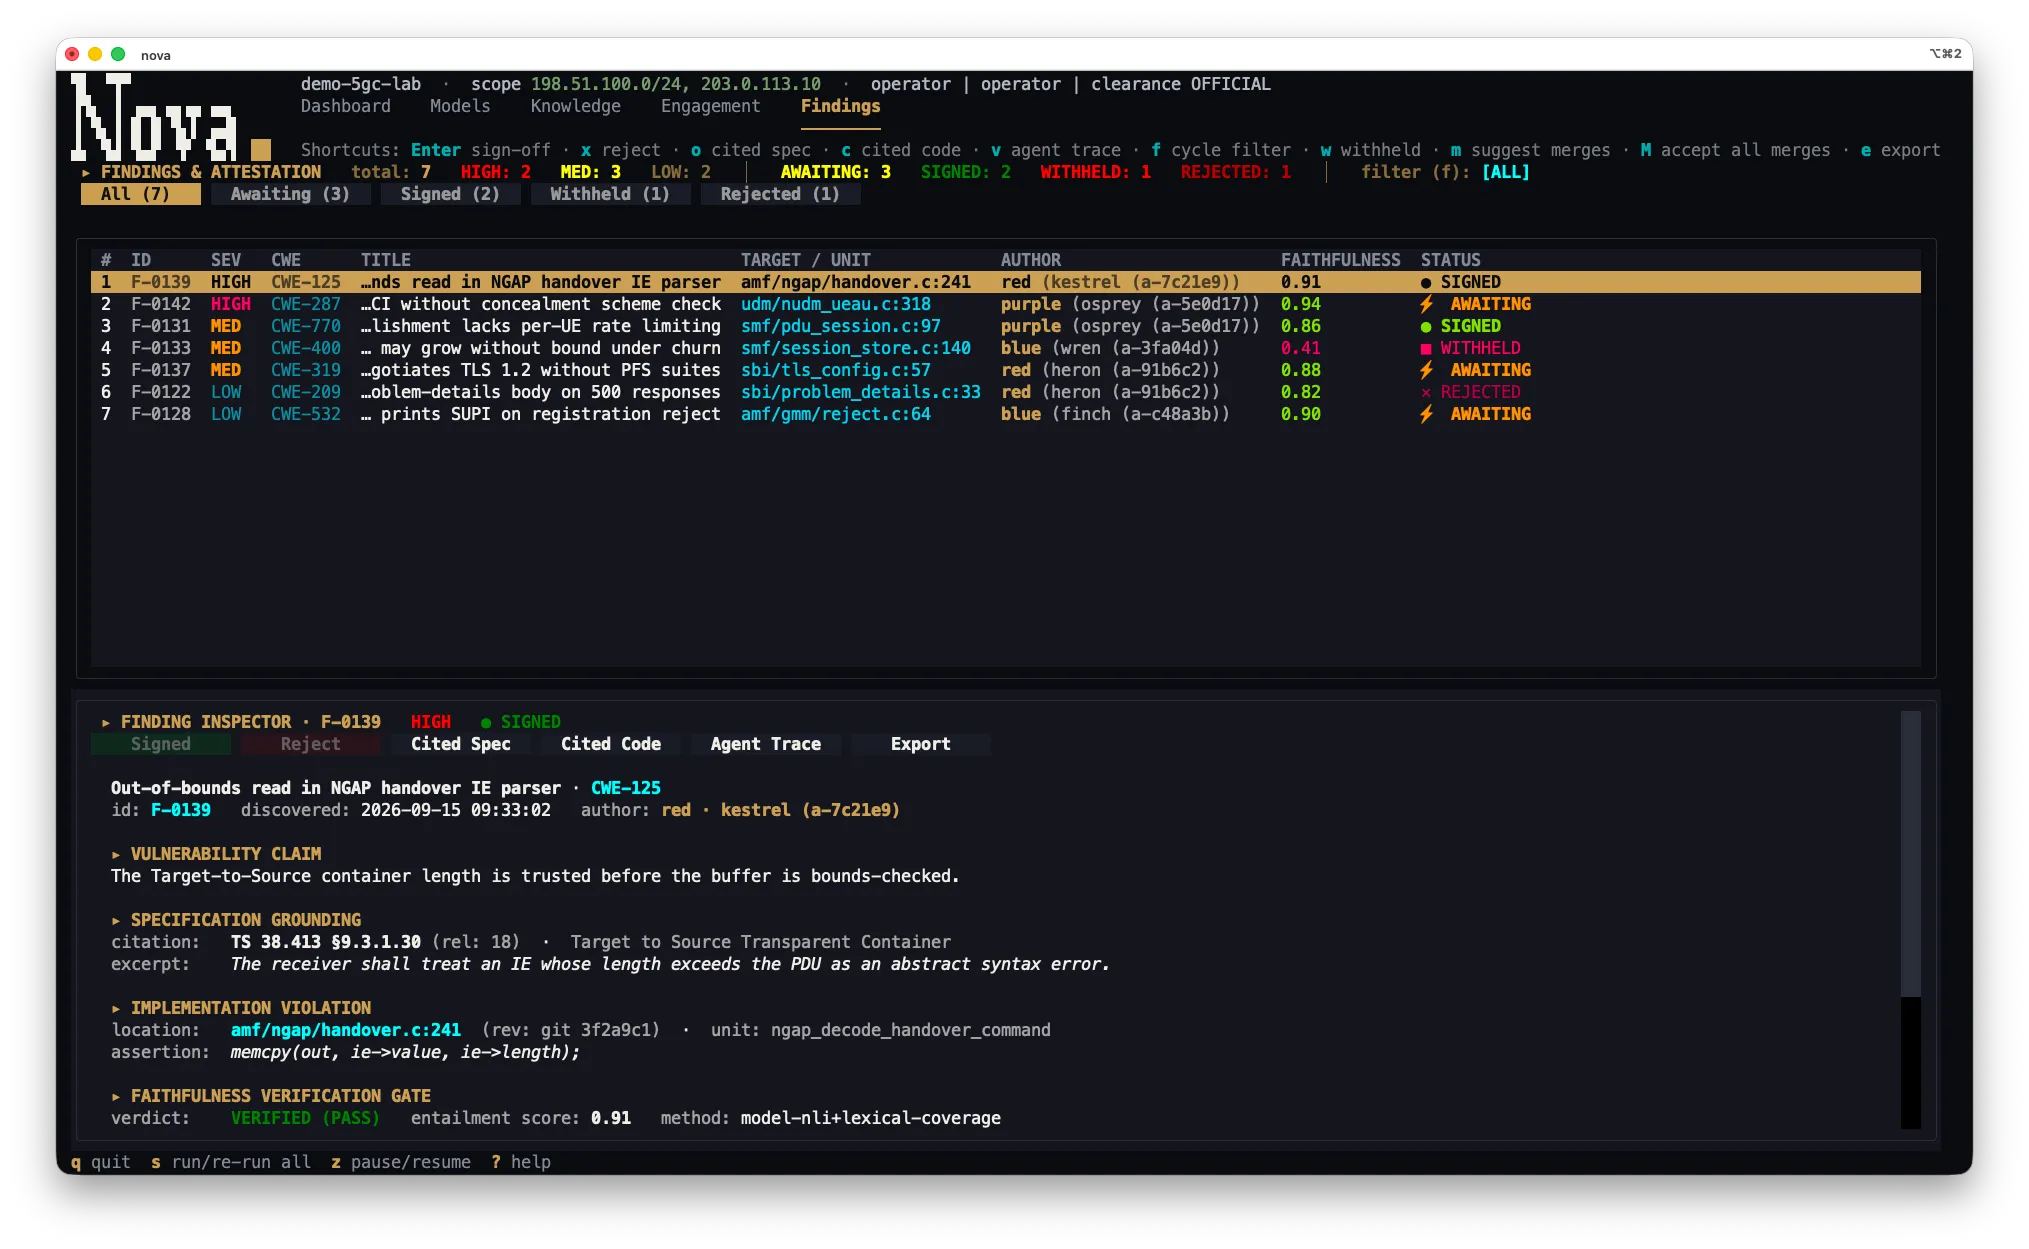
Nova terminal interface, Findings view: Each finding grounded in a clause and a code line, awaiting sign-off
Findingsassets/screens/5.webp
The gap01 / 09

Today’s AI testing platforms share one blind spot

Cloud-first platforms

Cloud SaaS by designclient data leaves the environment
Shared or vendor-hosted modelsthe provider holds the weights
Excellent breadth and coveragethat a classified site cannot deploy

The buyer nobody can serve

Defence, intelligence, critical infrastructure and regulated operators need exactly this capability, yet cannot send their source, specifications or attack surface to a third-party cloud.

The capability exists. The trust envelope to deliver it on their terms does not.

Nova closes that gap: the same capability, on the client’s terms.

What Nova is02 / 09

The sovereign AI security platform your most sensitive clients can actually deploy.

Delivered as a bespoke engagement on a fixed, inspectable pipeline: Nova deploys a red and purple team agent system inside the client’s own environment, grounds every finding in the client’s own specifications, manuals or documented code, and hands each finding to a cleared human to sign. Purple agents reproduce red’s leads by running their test cases in a sandbox with no network. No specification corpus is required. Given a published advisory, it answers the question a client actually asks: is our code affected? It reads Python, Go and Rust today, with C and C++ in progress.

The differentiator03 / 09

A trust envelope the existing cloud platforms cannot enter

01 Runs on their metal

Fully on-premises and air-gappable. No client source, spec, finding or model weight ever leaves the environment.

02 No phone-home

Offline by construction: nothing calls out. The only traffic permitted is to the authorised target ranges, and licences are verified locally.

03 Model-independent & measured

Client-chosen open-weight models behind one uniform endpoint. None is enabled without a passing, measured behavioural passport.

04 Hardscope + human sign-off

The authorisation boundary lives in the sandbox, policy and tooling, not a prompt. Humans approve every agent and sign every finding.

Data flow04 / 09

One finding, end to end

A single finding traced from source to signed release, and the four gates that can stop it. Scroll to follow it through the pipeline.

Stage 01 / 07
01
Parse
spec + code → clause tree · code graph
02
Retrieve
dense + lexical  ·  clearance-filtered
03
Draft
targeted agent  ·  human-approved
04
Reason
red-team agent  ·  sealed sandbox
05
Enforce
policy gate  ·  default-deny
06
Verify
citation ⊨ claim  ·  code proof
07
Sign off
independent reviewer  ·  attested
↓Scroll to advance the findingFinding released: continue to enforcement
Finding

Missing mandatory IE validation on inbound message

Parsed fromTS 24.501 § 8.2.1 (Rel-17)  +  internal/gmm/handler.go
Retrievedclause chunk + code site, provenance-keyed
Agentbuilt for this finding’s code · approved by operator
ReasonedIE validation absent on the inbound path
Scope decisionin-scope · allowed · logged
Faithfulnesscitation ⊨ claim · no guard on path
ReleasedAttested · independent sign-off
Enforcement05 / 09

Scope held in infrastructure, not the model

Built from small, inspectable engines. The boundary holds independently of the model, whatever it has been told and however it has been tuned.

01

Sealed agents

Each agent runs in a gVisor sandbox with no network interface, a read-only root and dropped privileges. Its only channel to the host is a size-limited broker pipe.

02

Default-deny policy

Every tool call is checked against declarative, version-controlled policy: target within authorised IP ranges, code within authorised paths, tool per persona, time window and clearance. If the policy engine fails, agents halt.

03

Single tool gateway

Every tool sits behind one gateway, uniform across agents and personas. Denied calls fail closed, and every decision is written to a hash-chained, tamper-evident audit log.

04

Egress control

Outbound traffic is allow-listed to the authorised target ranges by IP, with no DNS resolution. Nothing else leaves the environment.

An adversarial scope-escape suite of 27 probes (out-of-scope and adjacent addresses, loopback and cloud-metadata pivots, DNS names, IPv6, path traversal, privilege escalation, prompt injection, escapes from sandboxed test code, a licence check that phones home, and a failed policy engine) runs in CI and at install as a release-blocking gate.
Model assurance06 / 09

Every model ships with a measured passport

Nova never claims a model is “clean”, a claim nobody can prove. It proves what it can measure: each model is scored on the exact serving stack it will run on, a modified model is compared with its own unmodified baseline, and no model is enabled without a passing passport.

General reasoning and knowledge
Code comprehension
Security-domain tasks
Tool-calling reliability (release-gating)
Hallucination
Distributional drift

Every delta carries a 95% confidence interval. Deploy only when the client’s go / no-go thresholds are met.

Model passport*example
Reasoning retained97%
Security tasks retained94%
Tool-call reliability91%
Hallucination increase+6 pts ±2 (95% CI)

* Illustrative example only.

Governance & evidence07 / 09

Humans approve the agents and sign the findings

Nova drafts; people decide. Every step leaves evidence a client, auditor or regulator can check.

Targeted agent drafting

Nova aims each agent at specific code: where a published advisory points, an entry point where untrusted input reaches a sensitive operation, or the directories an operator chooses, grounded in the requirement that governs it.

Agent Review Gate

No drafted agent runs until an operator has inspected its objective, tools, budget and citations, and approved it.

Separation of duties

Whoever runs an engagement cannot sign off its findings. Sign-off is a cryptographic signature over the finding’s content.

Reproducible citations

Each finding cites the exact clause and release, and the exact code line and source revision, so an independent reviewer can check it.

Standard deliverables

SARIF 2.1, STIX 2.1, NIST OSCAL, ECS for SIEM, CSV and a readable report, with ISO/IEC 27001, NIST SP 800-53 and UK MoD Def Stan profiles.

Verifiable close-out

At the end of an engagement, working keys are destroyed and working data with them. The signed audit trail and deliverables are kept.

Deployment08 / 09

Built for your environment

On-prem, air-gapped

Runs entirely on client-owned hardware and their on-prem GPUs.

Runtime-portable

Docker or Podman Compose, rootless Podman Quadlets, or Kubernetes, all generated from one topology.

Terminal-native

A full TUI over SSH, like a modern coding agent, with no heavy console.

Offline licensing

Signed licences verified locally, with seats bound to named people. An expired licence never locks you out of your own data.

Inspectable stack

A dependency-minimal core and open-weight models; no proprietary black box the client cannot audit.

GPU serving pools

Deploy, resize and retire model pools on the client’s cluster from the terminal, or attach an OpenAI-compatible engine the client already runs inside the enclave.

For the buyers who cannot use anything else

Organisations that are simultaneously high-value targets and forbidden from cloud security tooling.

Defence & intelligence

Classified systems that cannot touch a third-party cloud.

Critical infrastructure

Energy, transport and industrial control operators.

Telecom / 5G core

Specification-heavy stacks where findings map to exact 3GPP clauses.

Regulated finance

Proprietary code under strict data-residency regimes.

Healthcare & public sector

Sensitive data with hard sovereignty requirements.

Where Nova sits09 / 09

Built for the rooms others cannot enter

Autonomous testing platforms do valuable work at cloud scale. Nova is built for the environments they are not allowed into.

Cloud platforms offer breadthand continuous coverage.
Nova offers the sovereign trust envelopethat a cloud delivery model cannot provide.
A bespoke, high-trust engagementfitted to the client’s stack and clearance model.

Bespoke build, licensed platform, retained support

Build

Engagement fee

Design, integration and tuning of the pipeline to the client’s stack, knowledge base and clearance model.

Licence

Per-seat · offline

Time-limited licensing of the whole platform on the client’s own hardware, verified locally, with seats bound to named people.

Support

Retainer

Updates delivered offline, new-model onboarding and passports, and continued red and purple team operation.

Optional: hand-curated knowledge bases for the highest-value targets. Every engagement is authorised, scoped in writing and enforced by the platform itself.

Founder·
Dr Andrea Tassi

Dr Andrea Tassi

Former Chief Engineer at Samsung Research UK and an IEEE Senior Member, bringing hands-on command of the spec-driven, high-assurance systems Nova is built to test.

50+peer-reviewed publications
IEEESenior Member
Awardedmultiple best-paper prizes
Book a call Open in a new tab

Loading the booking calendar. If it does not appear, open cal.com/agentnovauk/30min.

The one thing to remember

Cloud platforms cannot enter the room where your most sensitive systems live. Nova can.

Engagements are scoped directly with the founder, under authorisation, on your hardware.

Book a call